For B2B software teams facing audits and security reviews
Compliance automation that keeps you audit‑ready.
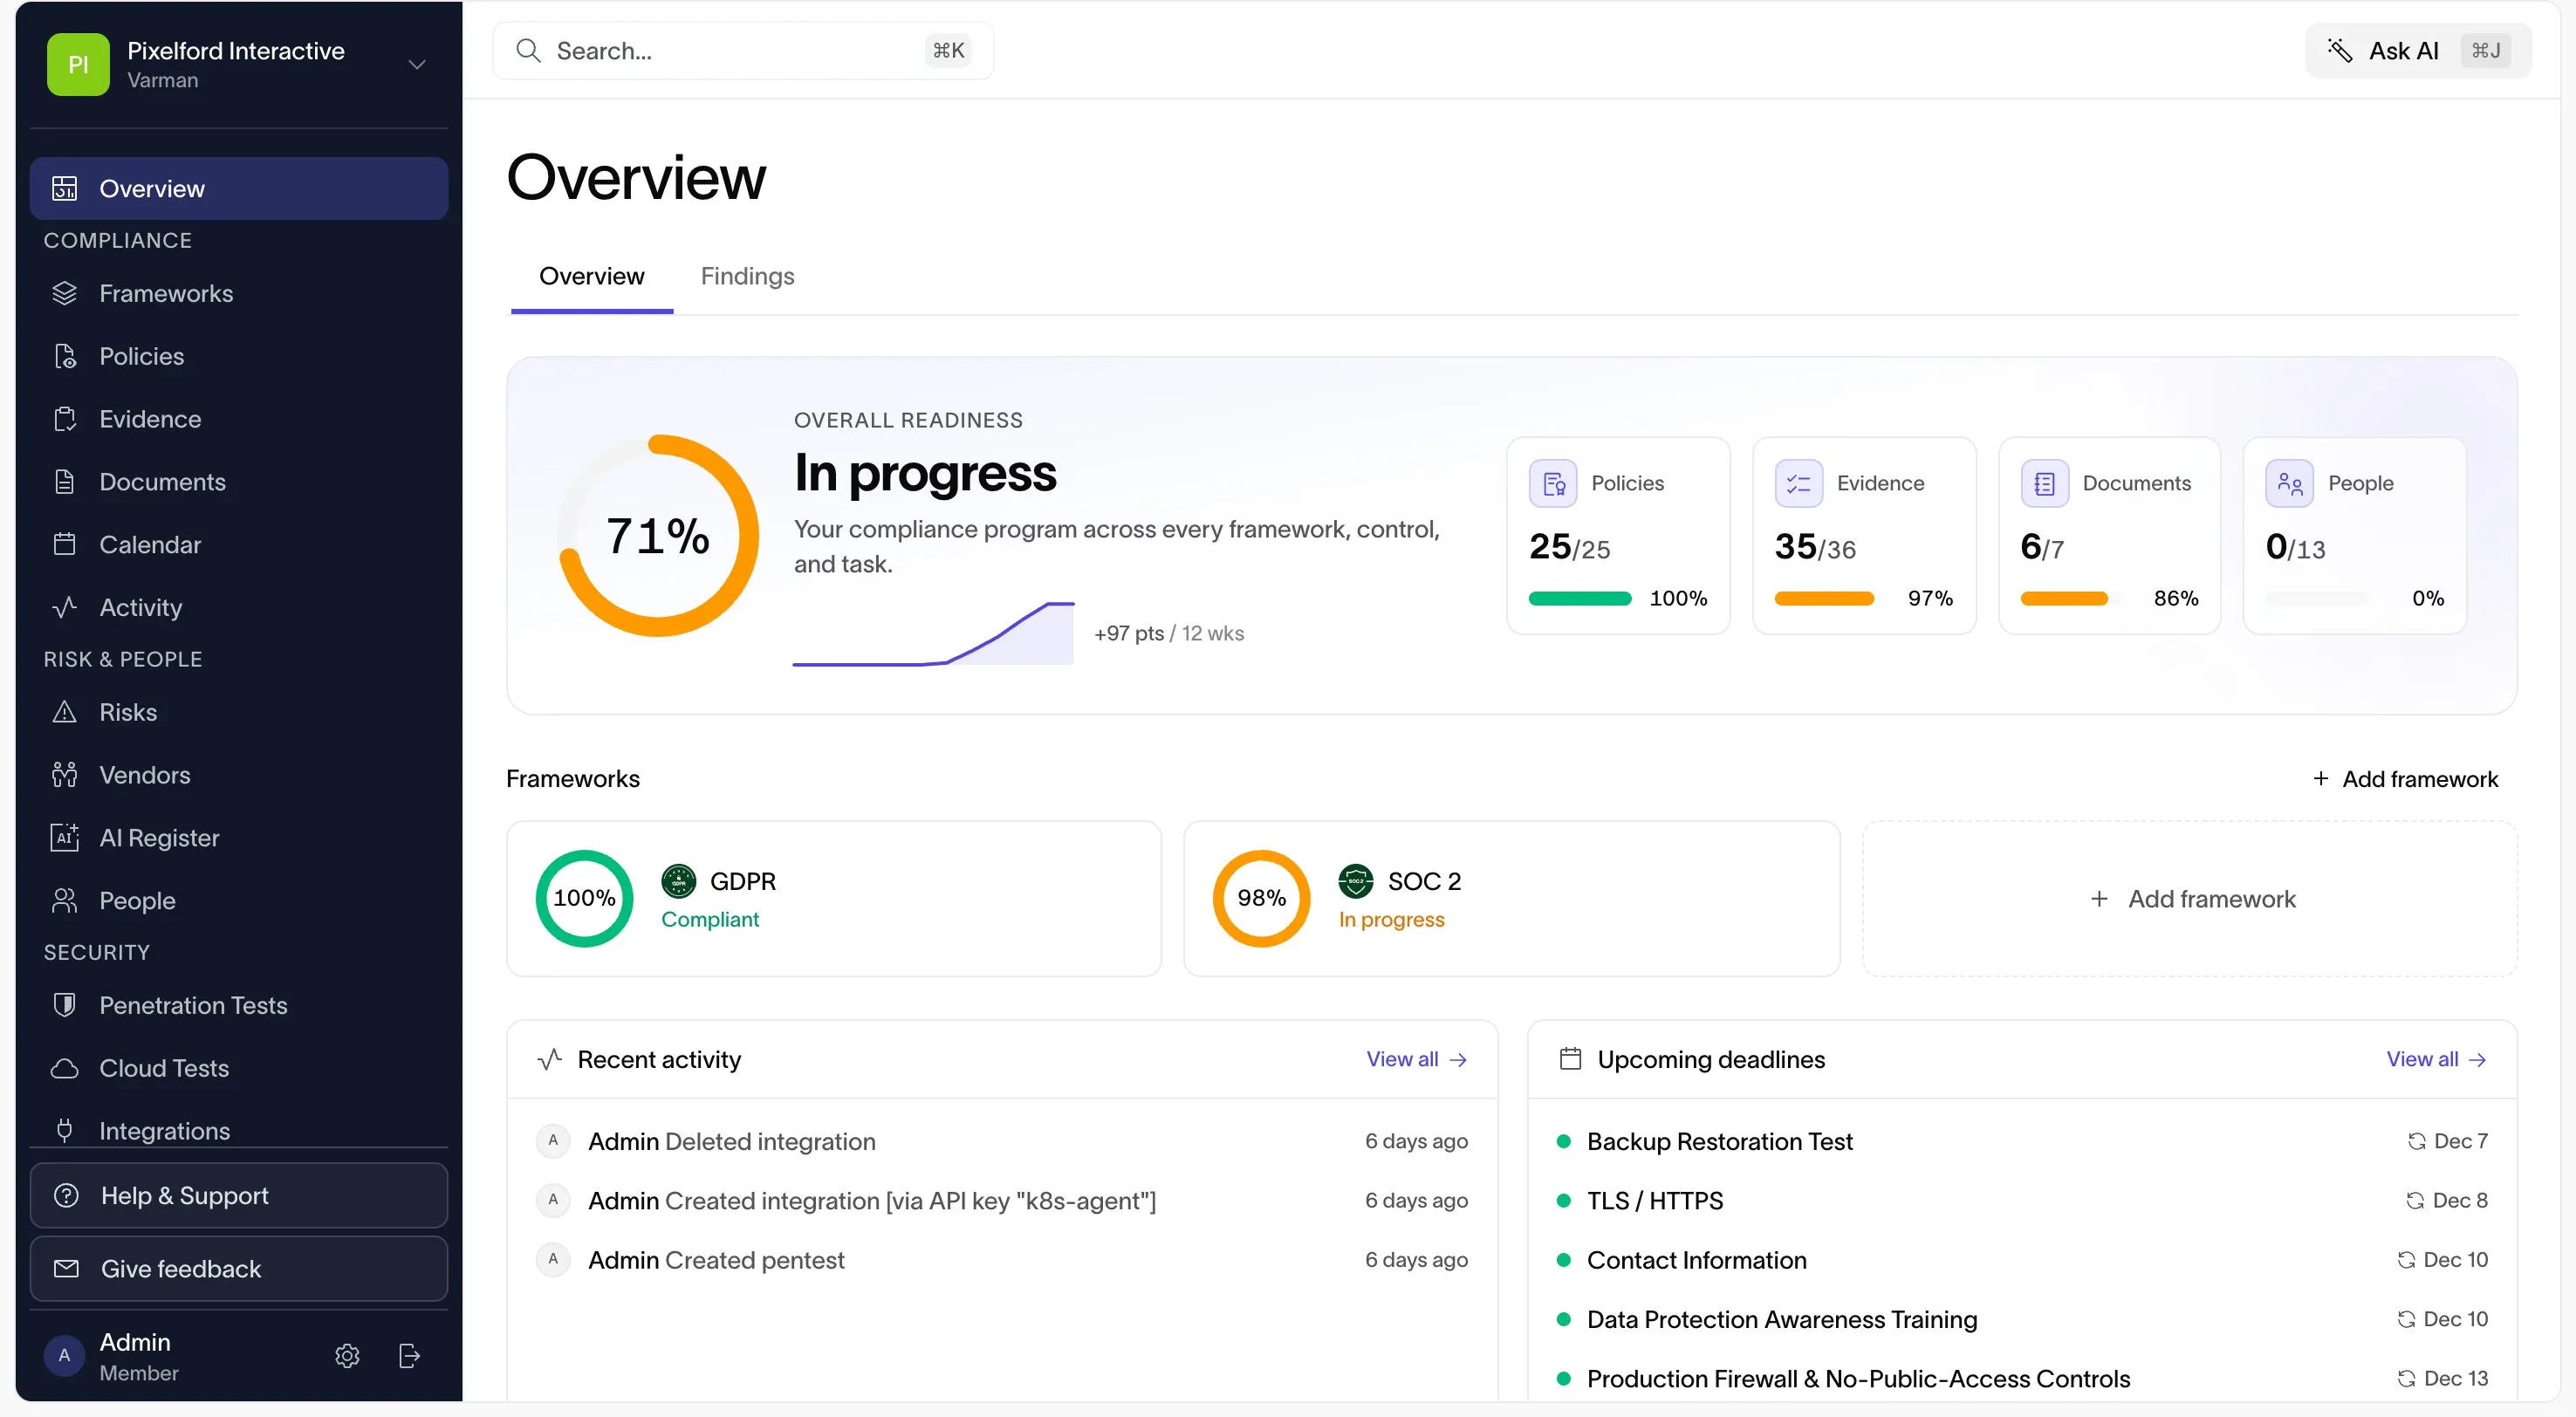
Varman connects to your cloud, code, and identity tools, collects evidence for SOC 2, ISO 27001, HIPAA, and 16 other frameworks, and monitors every control between audits. Penetration testing, AI governance, and phishing simulation come in the same plan.
Checks run against the tools you use
Six tools you would otherwise buy separately.
Each one shares the same controls, evidence, and people, so a pentest finding or an AI system lands in your program instead of in another vendor's dashboard.
- Compliance automationEvidence collected from your stack and mapped across 19 frameworks on one control set.
- Penetration testingOn-demand or scheduled tests, with findings ranked by severity and kept beside your controls.
- AI governanceAn AI System Register with EU AI Act risk tiers, plus the ISO 42001 framework.
- Phishing simulationDifficulty-graded campaigns whose results count as security-awareness evidence.
- Trust CenterA public page for your security posture, with document access after approval and NDA.
- Questionnaire draftingBuyer questionnaires answered from your own policies and evidence, reviewed by you.
Stop stitching a tool to every audit question.
Most teams assemble compliance one purchase at a time. Here is what that usually looks like, next to the same jobs done in Varman.
| The job | Stitched-together stack | Varman |
|---|---|---|
| Framework compliance | Stack:A GRC or compliance tool, often scoped to the frameworks you buy | Varman: 19 prebuilt frameworks sharing one control set |
| Penetration testing | Stack:An outside firm, booked once a year, with findings delivered as a PDF | Varman: Tests on demand or on a schedule, findings tracked next to controls |
| AI risk | Stack:A spreadsheet of AI tools, updated when someone remembers | Varman: AI System Register with EU AI Act risk tiers and ISO 42001 |
| Security awareness | Stack:A separate phishing simulation product | Varman: Phishing campaigns whose results attach as training evidence |
| Security questionnaires | Stack:A questionnaire tool, or copying answers from the last one | Varman: Drafts from your own policies and evidence, in the app or in Chrome |
| Trust Center | Stack:A trust portal from yet another vendor, or documents over email | Varman: A public Trust Center with NDA-gated document access |
| Where it all lives | Stack:Several logins, with evidence copied between them by hand | Varman: One platform, one data model, one plan |
Weighing a specific vendor? Read the side-by-side comparisons, with sources.
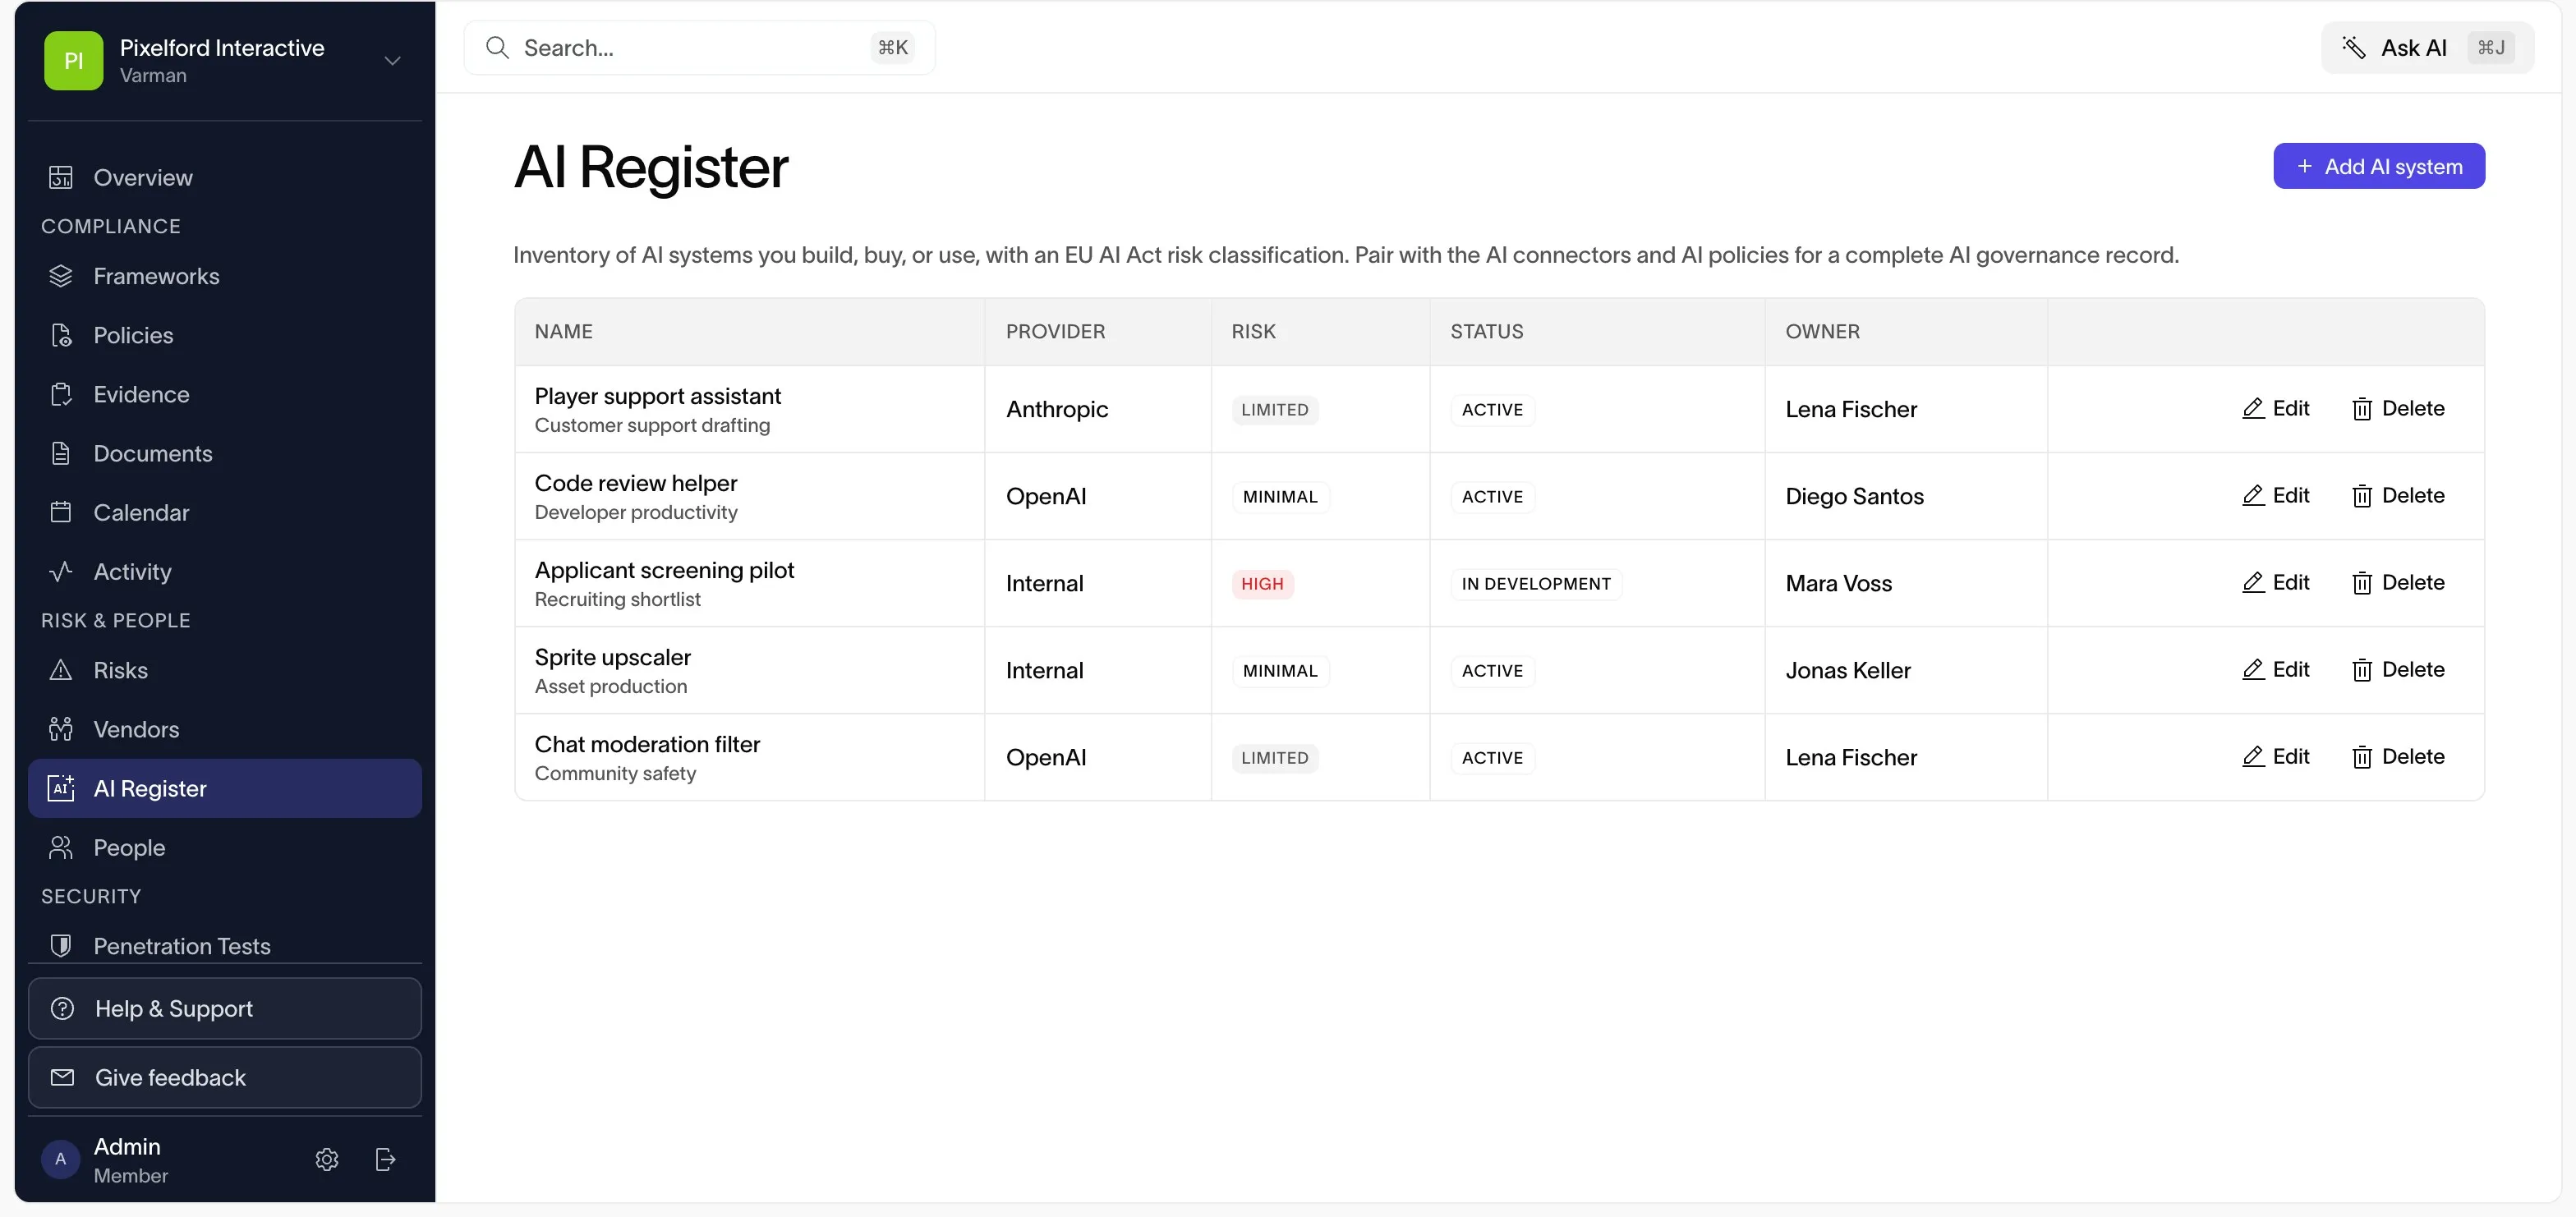
Govern the AI you build and the AI you buy.
Every AI tool your team adopts is a new risk and a new audit question. Varman keeps an AI System Register, classifies each system against EU AI Act risk tiers, and ships AI policy templates alongside the ISO 42001 framework.
- AI System Register with owner, purpose, and lifecycle
- EU AI Act risk tiers: unacceptable, high, limited, minimal
- Connectors that inventory OpenAI and Anthropic access
- ISO 42001 framework and AI policy templates
Every control counts toward every framework.
Satisfy a control once and it applies everywhere it is referenced. Watch readiness climb per framework as evidence lands, with a clear view of what is met and what remains.
Browse frameworks →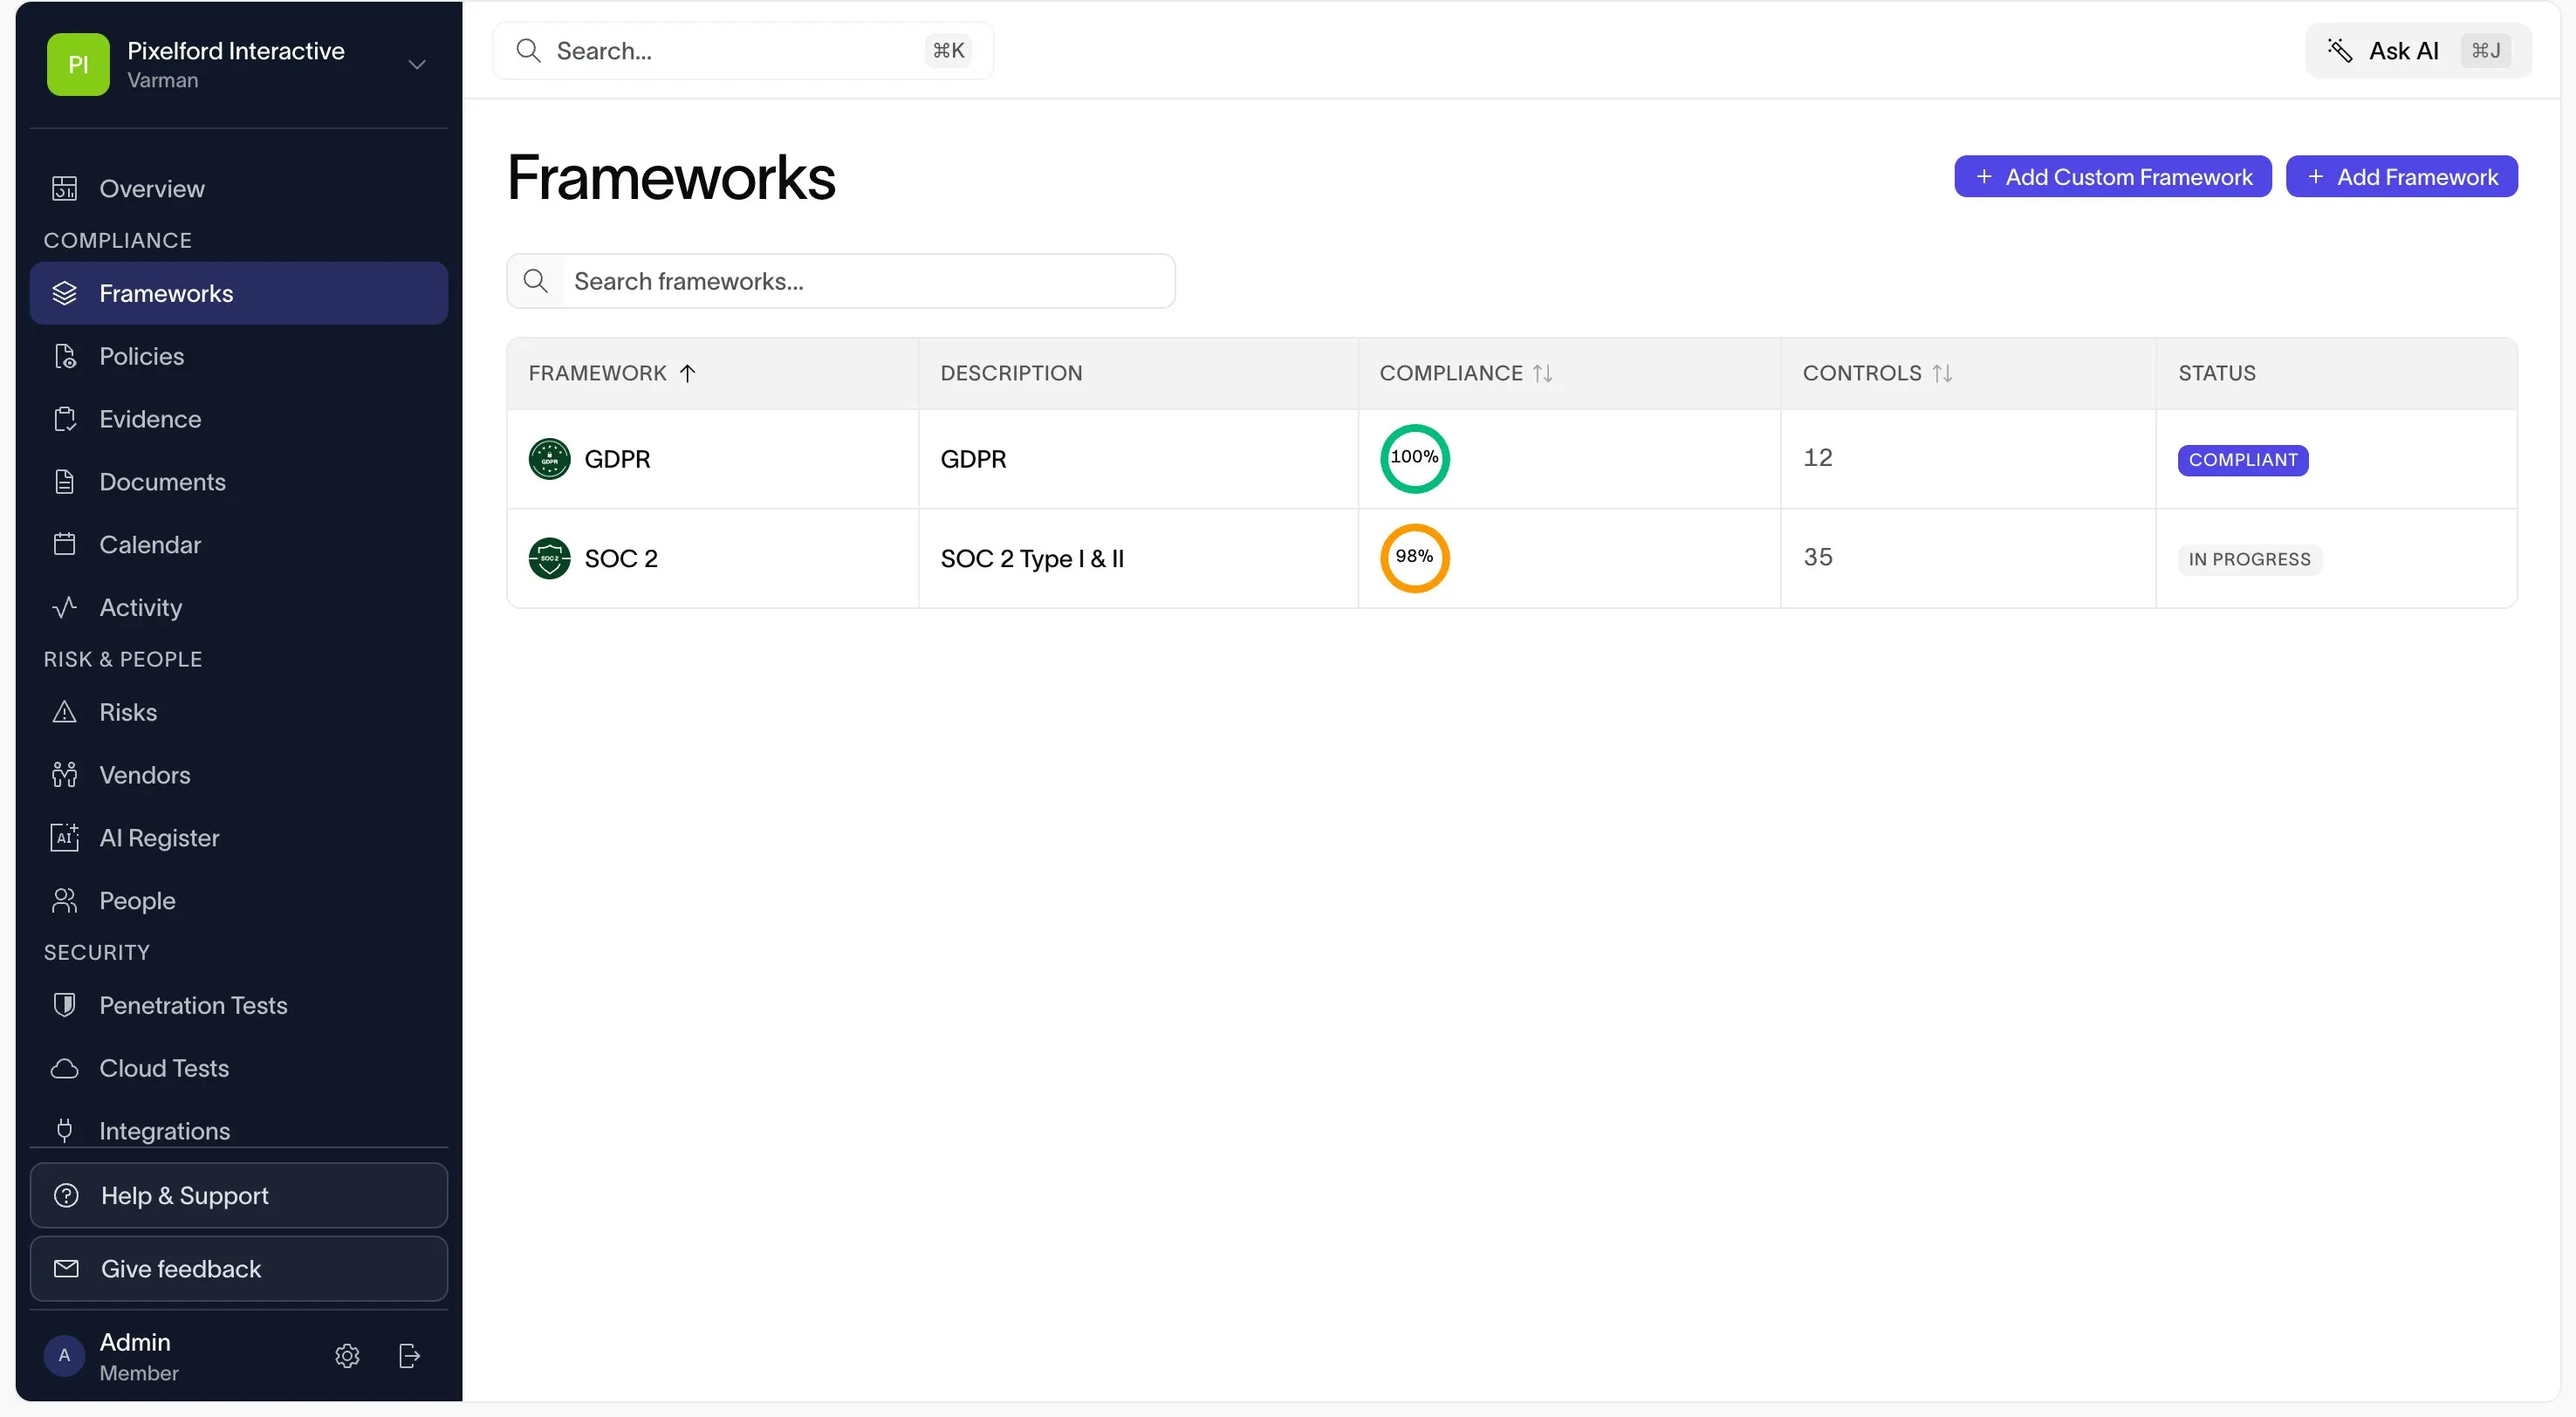
 SOC 263 requirements
 ISO 27001119 requirements
 GDPR19 requirements
 HIPAA77 requirements
 ISO 4200170 requirements
 NIST 800-171110 requirements
 NIST CSF106 requirements
 PCI DSS233 requirements
 NIS 2160 requirements
 CMMC L2110 requirements
 ISO 900137 requirements
 CCPA12 requirements
 PIPEDA10 requirements
 DORA98 requirements
 EU AI Act73 requirements
 ISO 27701109 requirements
 ISO 2230145 requirements
 Cyber Essentials37 requirements
 Essential Eight24 requirements
- Compare all frameworks →
Penetration testing inside the platform.
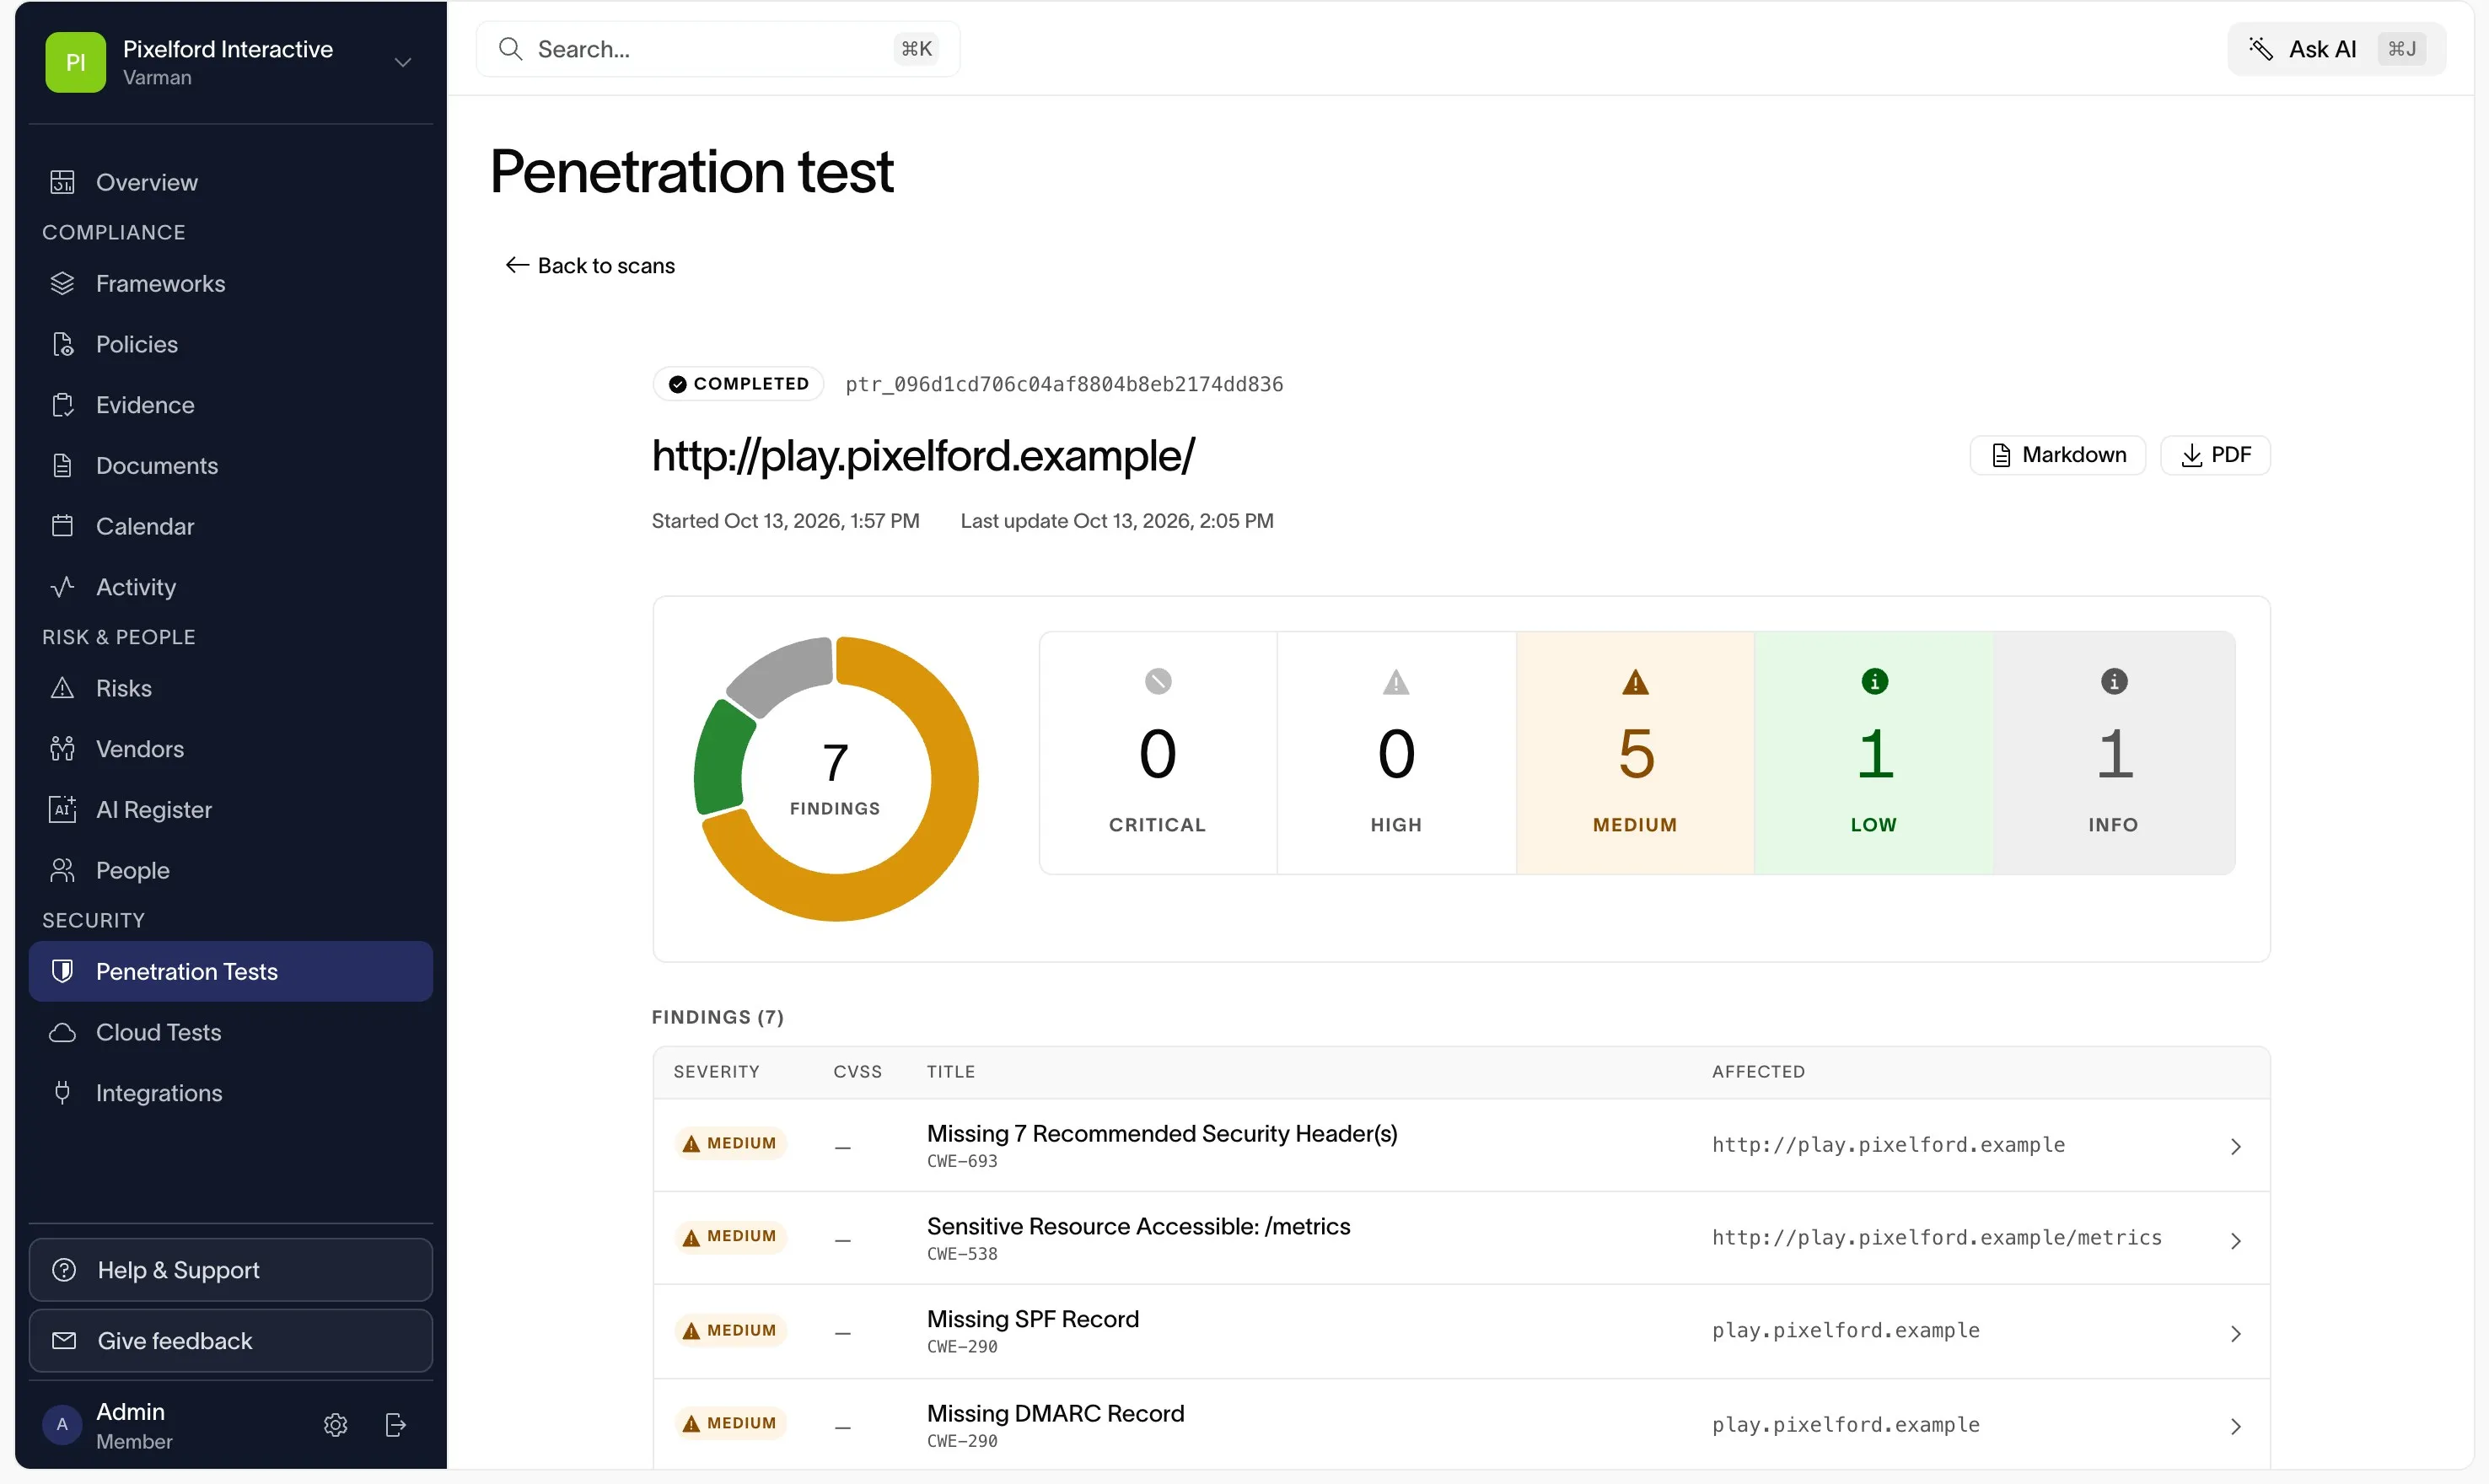
Point a scan at a URL you own and run it on demand or on a schedule. Results land in the same platform as your controls, so a test feeds your program instead of producing a PDF that goes stale the day it arrives.
- Findings ranked by severity, each with its CWE reference
- Affected URL and detail for every finding
- Report export as PDF or Markdown
- Recurring schedules for repeat testing
The scan target shown is a deliberately vulnerable practice app.
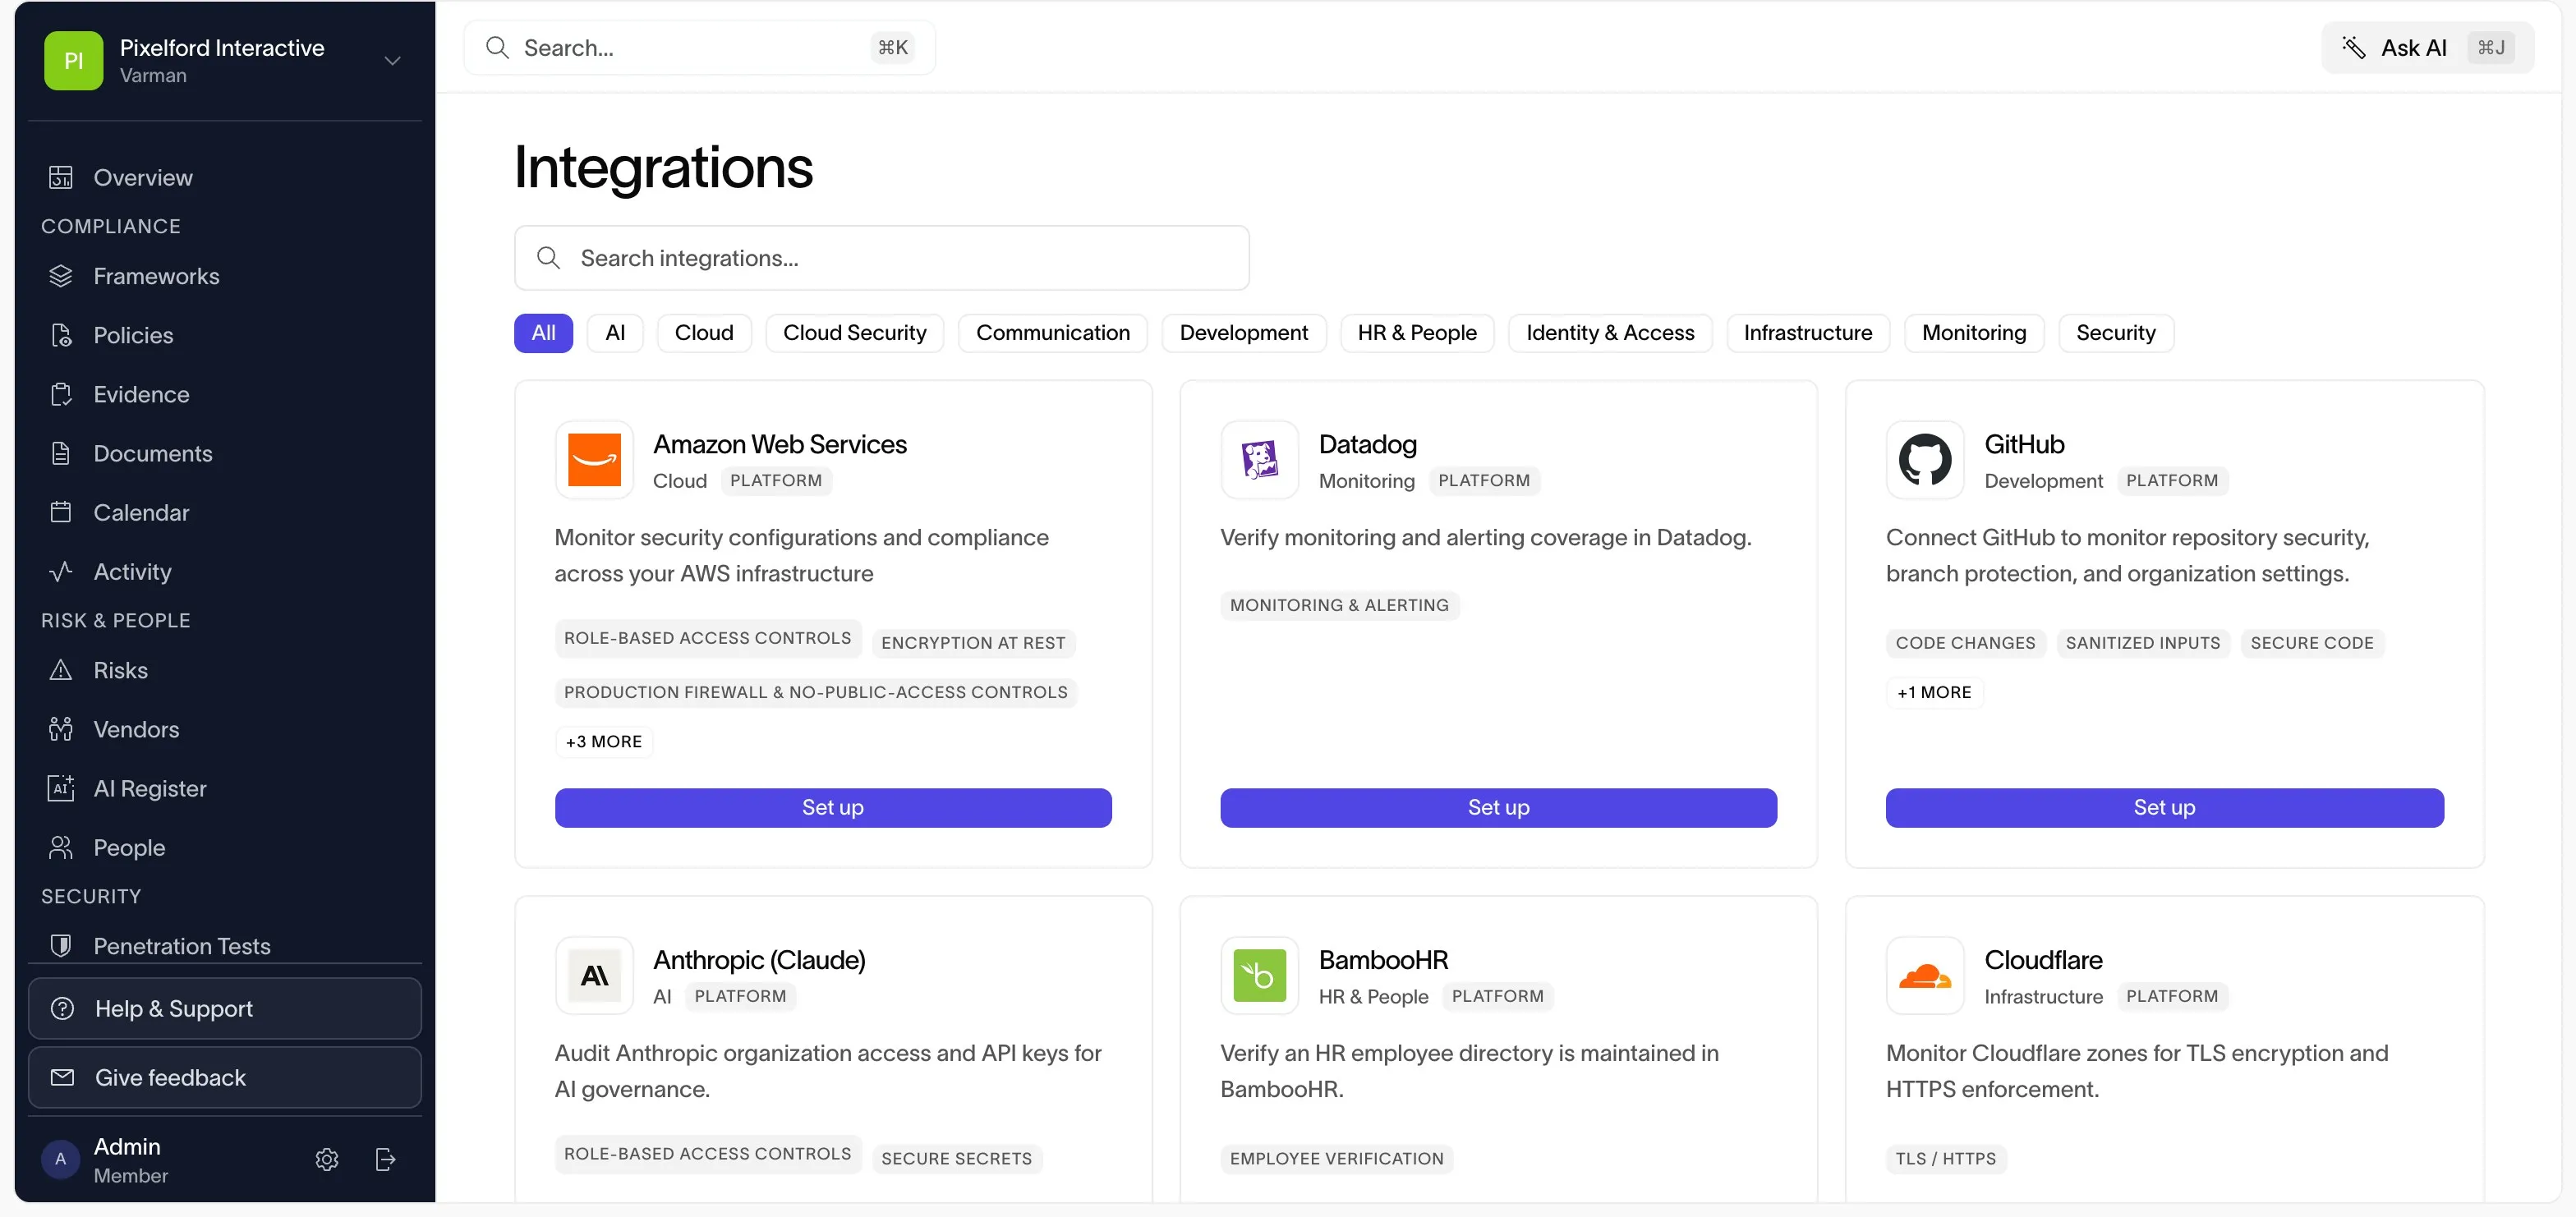
Switch on an integration yourself.
Cloud, code, identity, HR, monitoring, and your AI providers. Self-serve credentials, continuous checks, evidence mapped to controls automatically.
23 integrations, 64 checks. Each check is documented: what it looks at, when it fails, and how to fix it.
Browse all integrations →From first SOC 2 to many frameworks.
Land your first SOC 2 without a security team.
- Start with one framework
- Policy templates ready to adopt
- Questionnaire answers drafted for you
Run several frameworks without several tools.
- Multiple frameworks on one control set
- Penetration testing in the same platform
- Custom roles and RBAC
Assurance, scale, and controls your auditors trust.
- Custom and in-house frameworks
- Custom roles, RBAC, and audit logging
- API and hosted MCP server
Four steps, then it runs on its own.
- 01
Connect
Link cloud, identity, code, and HR with native integrations.
- 02
Map
One control set maps across SOC 2, ISO 27001, GDPR, HIPAA, and ISO 42001 at once.
- 03
Monitor
Evidence collects on a schedule. Failing controls and stale tasks surface on their own.
- 04
Attest
Hand auditors a clean, current evidence room, pentest findings and AI risk included.
Compliance automation, answered.
What is compliance automation?
Compliance automation software connects to your cloud, identity, code, and HR systems, runs checks on a schedule, and keeps the results as evidence mapped to the frameworks you need, so audit prep stops being a manual scramble.
Which frameworks does Varman support?
Varman has 19 prebuilt frameworks, including SOC 2, ISO 27001, GDPR, HIPAA, ISO 42001, PCI DSS, NIS 2, NIST 800-171, and CMMC Level 2. They share one control set, so evidence collected once counts toward each of them.
Does Varman include penetration testing?
Yes. You can run penetration tests against applications you own from inside the platform, on demand or on a schedule, and findings are tracked next to the rest of your program.
Is Varman an auditor?
No. Varman organizes your controls, policies, and evidence. Audits, attestations, and certifications are carried out by independent third parties such as CPA firms and accredited certification bodies.
How is Varman different from Vanta or Drata?
Compliance, penetration testing, and AI governance sit in one platform and one plan. See the side-by-side comparisons, with sources, on the compare pages.
Get audit-ready, and stay that way.
See how Varman automates your frameworks, pentests, and AI governance in one place.